Part 4: access, secrets and evidence

Scroll or pinch to zoom, drag to move, double-click to zoom in 100% SVG PNG Back to the post
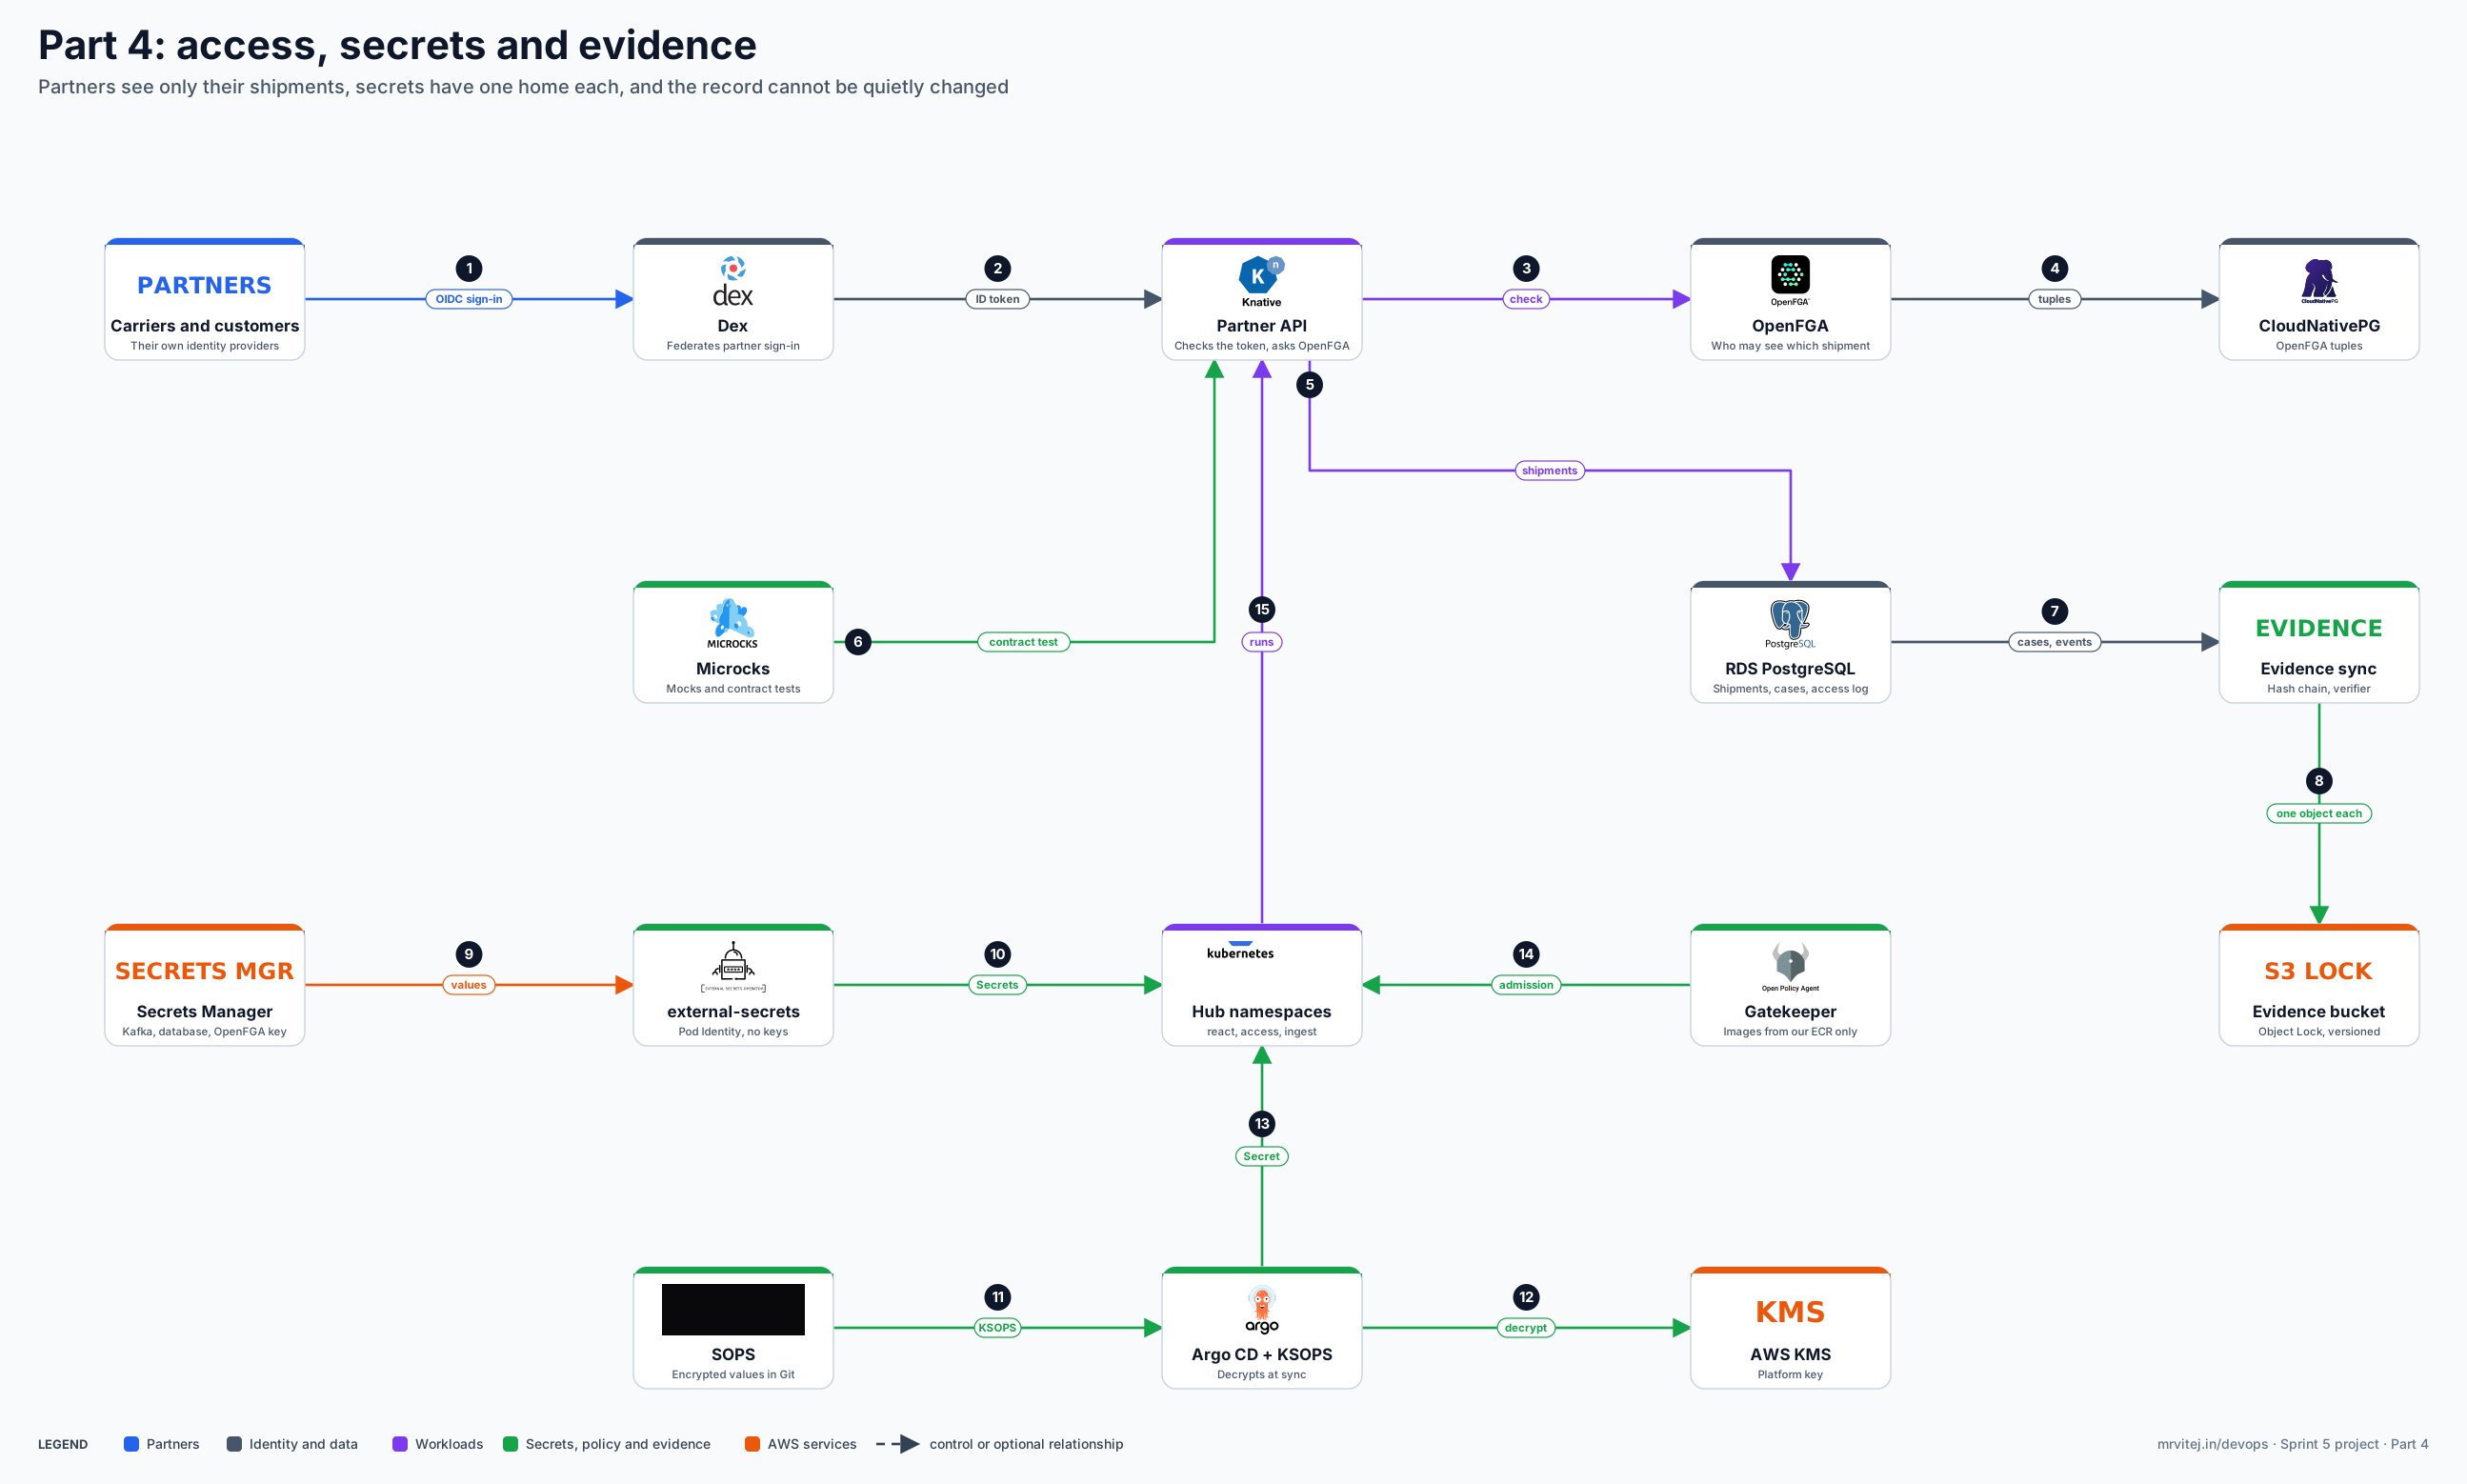
Architecture: carriers and customers sign in through their own identity providers, which Dex federates, and call the partner API with an ID token. The partner API verifies the token, asks OpenFGA whether the caller may see the shipment and reads shipments from RDS for PostgreSQL. OpenFGA keeps its tuples in a CloudNativePG database. Microcks tests the partner API against its contract. An evidence job reads cases, geofence events and access denials from RDS and writes one object each to an S3 bucket with Object Lock, each record naming the hash of the one before. Secrets Manager values reach the cluster through external-secrets with Pod Identity; SOPS files in Git are decrypted by Argo CD with a KSOPS plugin and the KMS platform key; Gatekeeper admits only images from our ECR.