Pinniped architecture: one login for every cluster

Scroll or pinch to zoom, drag to move, double-click to zoom in 100% SVG PNG Back to the post
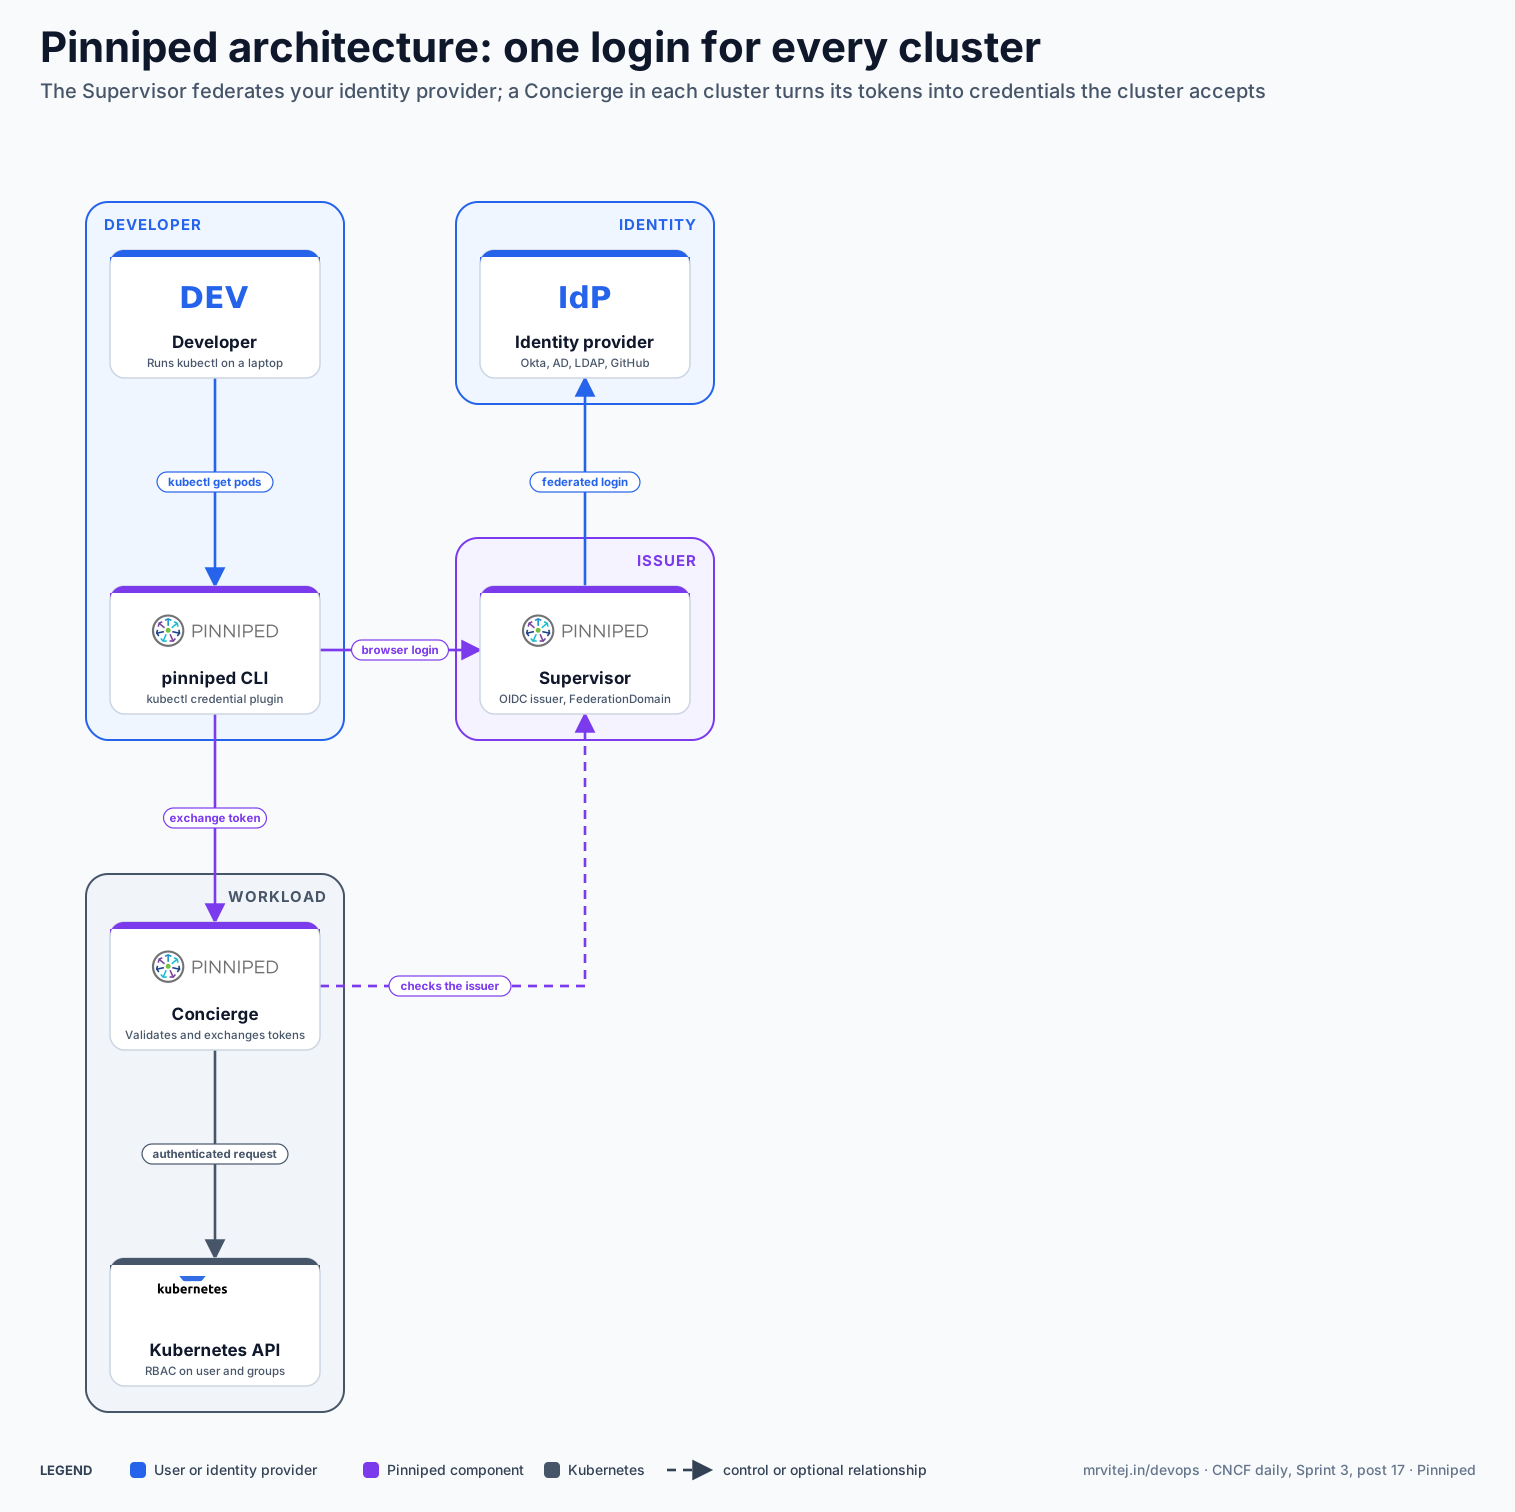
Pinniped architecture: a developer runs kubectl, which calls the Pinniped CLI as a credential plugin; the CLI logs in through a browser at the Supervisor, which federates to an identity provider such as Okta, Active Directory, LDAP or GitHub and issues tokens; the CLI exchanges the token at the Concierge in each workload cluster, which trusts the Supervisor issuer and lets authenticated requests through to the Kubernetes API server.