External Secrets flow: from a manifest to a Secret in a pod

Scroll or pinch to zoom, drag to move, double-click to zoom in 100% SVG PNG Back to the post
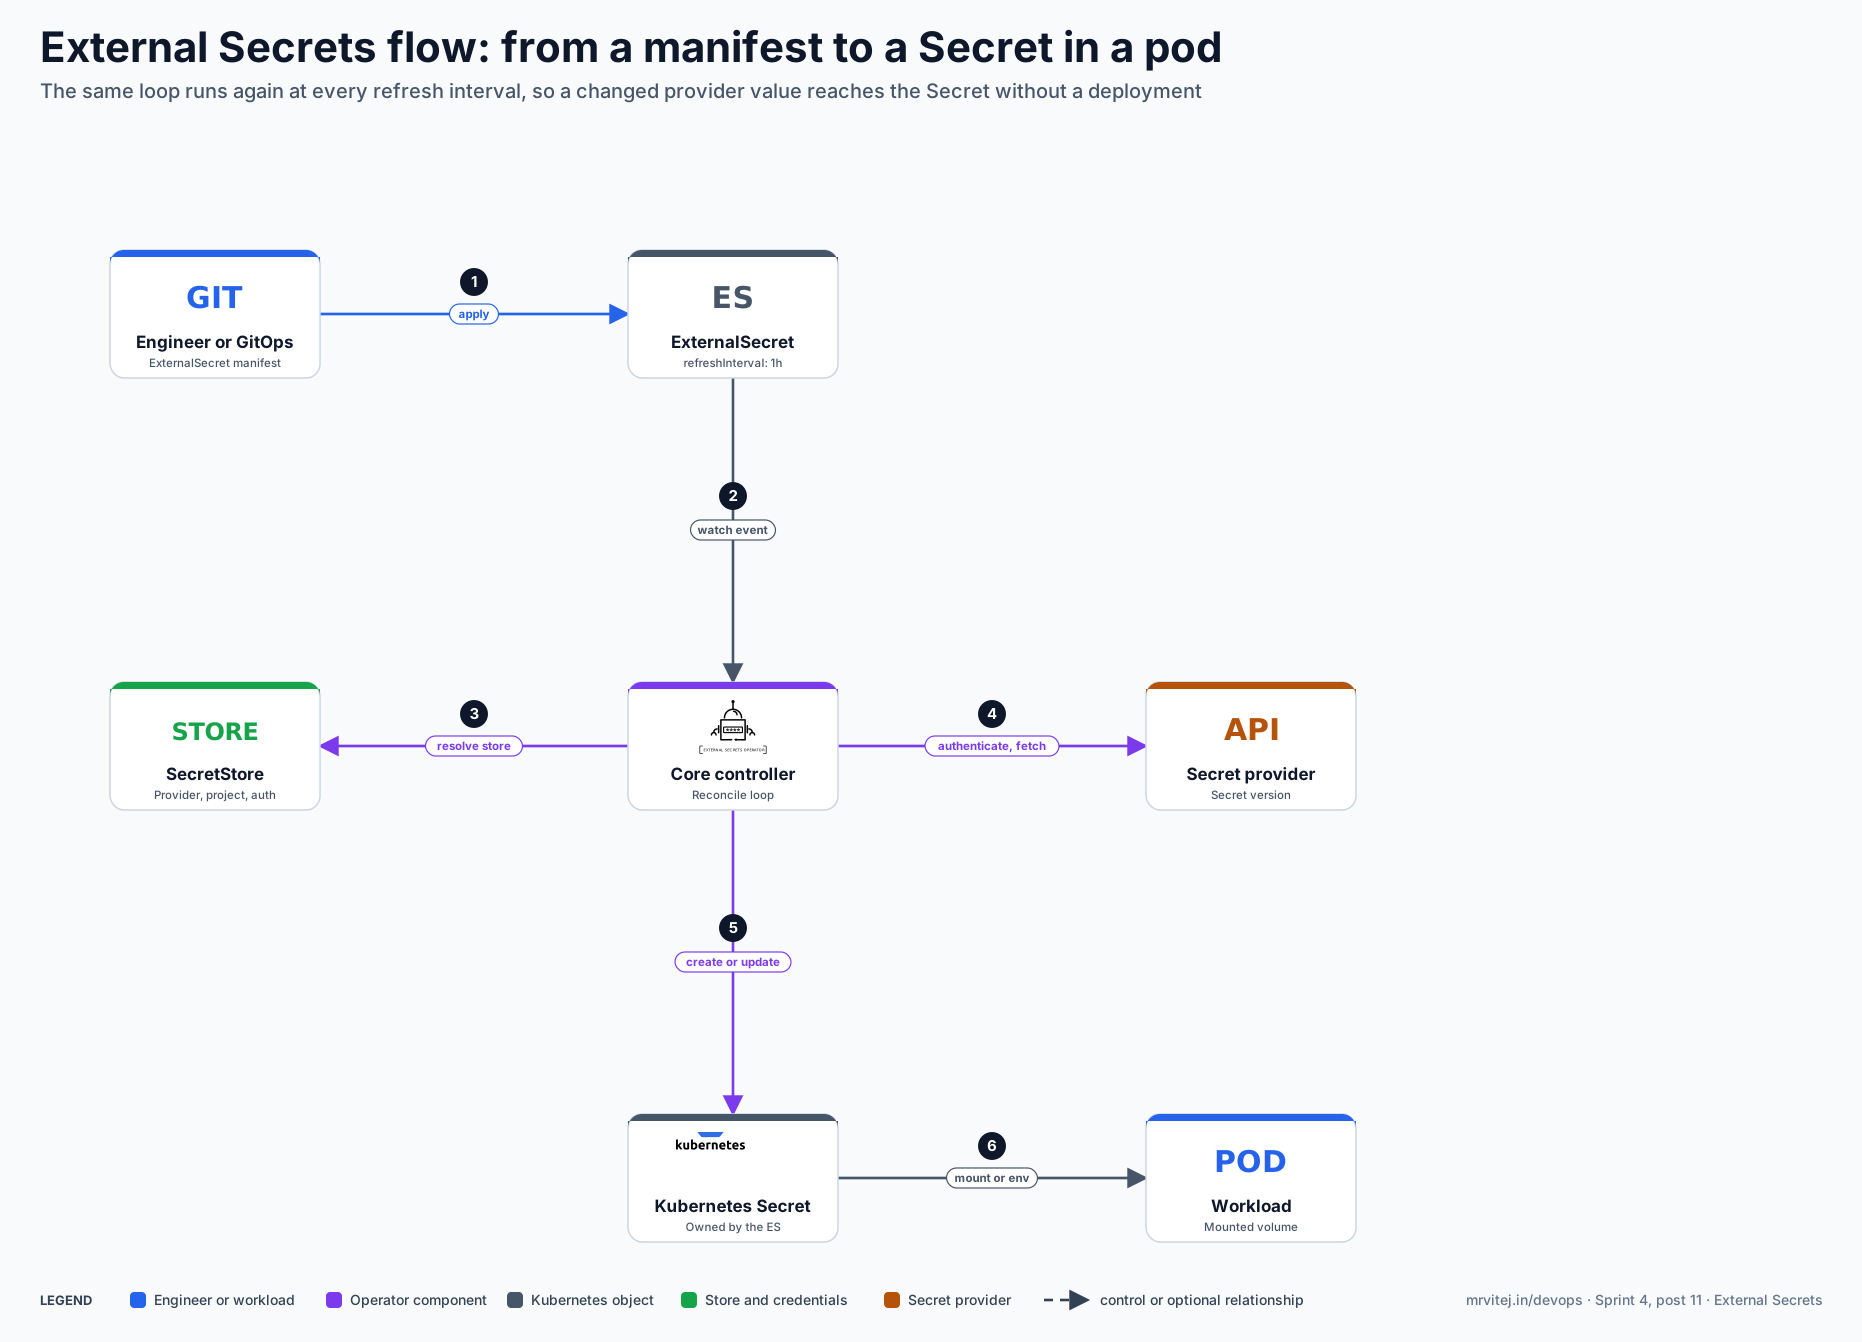
External Secrets flow in six steps: an engineer or GitOps tool applies an ExternalSecret; the core controller sees the watch event; it resolves the SecretStore the ExternalSecret references; it authenticates to the secret provider and fetches the values; it creates or updates the Kubernetes Secret from the template; a workload mounts the Secret as a volume or reads it as environment variables.