SOPS: secrets in Git, keys somewhere else

Scroll or pinch to zoom, drag to move, double-click to zoom in 100% SVG PNG Back to the post
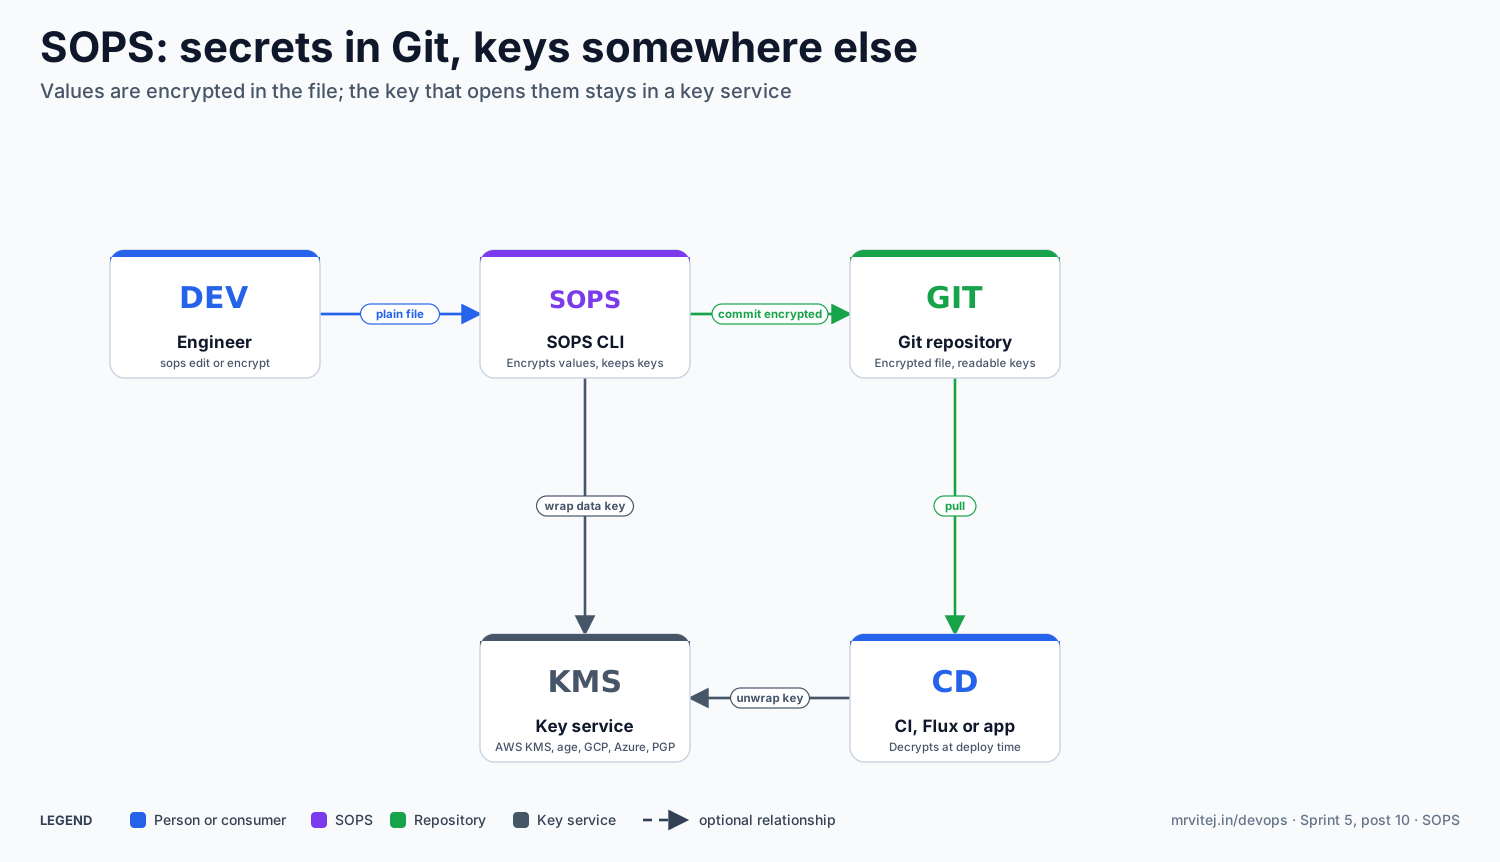
SOPS architecture: an engineer edits a secrets file with the SOPS CLI, which encrypts the values and leaves the keys readable, wrapping the data key with AWS KMS, age, GCP KMS, Azure Key Vault or PGP. The encrypted file is committed to Git. CI, Flux or an application later pulls it and asks the key service to unwrap the data key so it can decrypt.